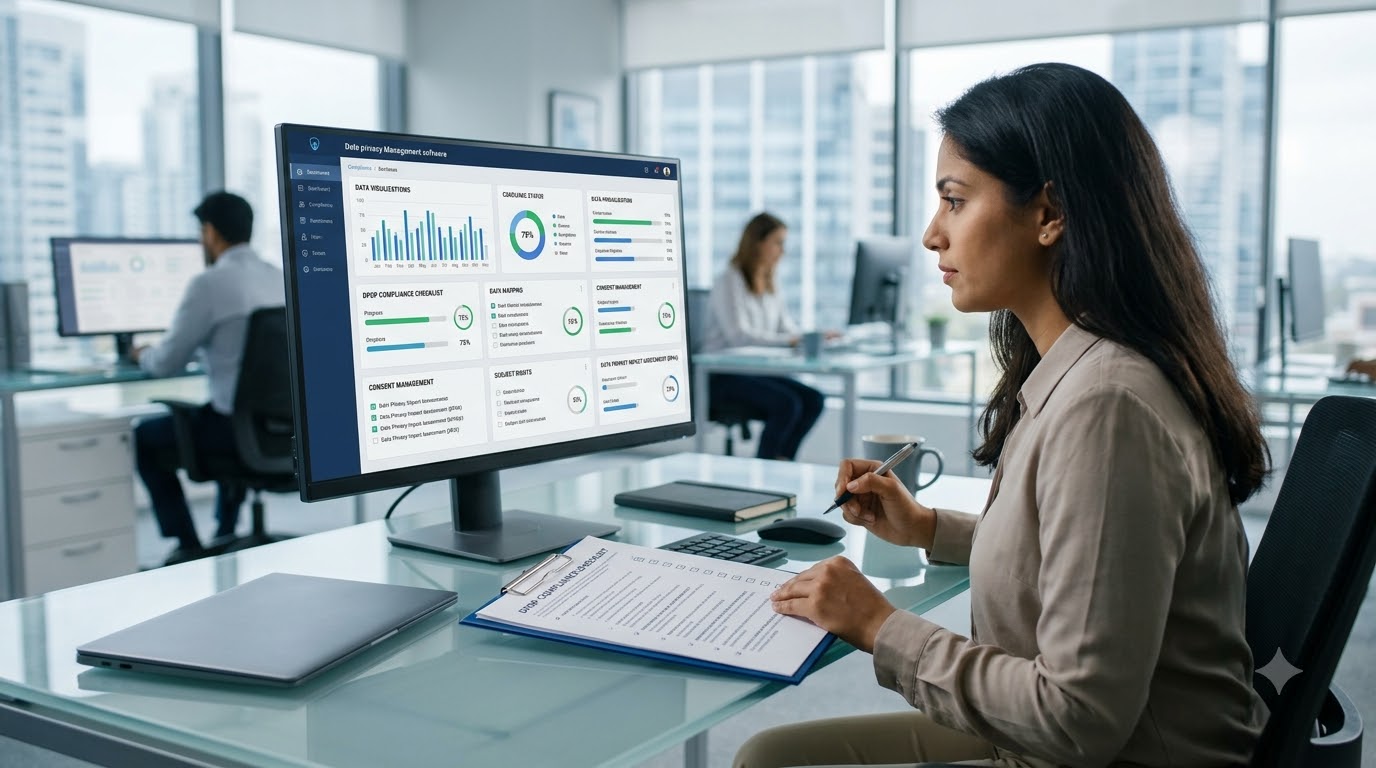
That's not a criticism of anyone looking for a simple answer. It's just that DPDP Compliance doesn't compress into a checkbox list the way a lot of people initially hope. What follows is the actual checklist — not simplified past the point of usefulness — along with an honest look at which items a privacy management platform genuinely automates, and which still need a human making a judgment call.
The checklist, item by item
1. Notice and purpose details. For each place you gather data, you should state a clear notice — what is taken, why it is taken, and how long you will keep it. Use plain language; don't hide it in a long privacy document most people never read. This is mainly a drafting job. A platform can help with templates and versioning, but the final wording should come from someone who knows exactly how you process the data.
2. Purpose-linked, granular consent. A blanket "I agree" doesn't meet the bar. Separate toggles for separate purposes — analytics, marketing, personalisation — each independently withdrawable. This is squarely automatable: a privacy management platform should handle capture, versioning, and withdrawal without manual intervention.
3. A consent entry that cannot be changed. It should show what was agreed to, the date and time, and which notice text was in effect. This can be handled by software — it is one of the few spots where a manual process, like updating a spreadsheet or a database field, cannot give proof that holds up when someone checks it closely.
4. Data principal rights fulfilment. Access, correction, erasure, grievance redressal, and nomination, each within a defined window. The intake and tracking are automatable; the actual correction or erasure sometimes requires a human to verify identity or resolve an edge case the system flags rather than silently completes.
5. The 48-hour pre-erasure notice. A specific, easy-to-miss operational requirement under Rule 8 — before erasure completes, the data principal gets advance notice. This is exactly the kind of scheduled, clock-driven task a platform should trigger automatically, because manually remembering a 48-hour window across dozens of requests is where things quietly slip.
6. Data discovery and mapping. You can't fulfil an erasure request, or answer a regulator's question, about data you can't locate. Scanning actual databases for personal data at rest is something a platform does structurally better than a manual audit ever could — this one's almost entirely automation's job.
7. Vendor and data processing agreements. Every third party touching personal data needs a current, valid agreement, and ideally, visibility into whether their access still matches what the contract allows. A platform can track expiry and flag mismatches; whether a specific contract's terms are actually adequate is still a legal review question.
8. Breach detection and dual-clock reporting. CERT-In's 6-hour window and the DPDP Board's separate notification timeline, tracked independently, from the moment an incident is logged. This is a case where manual tracking is not just harder but genuinely unreliable under the pressure of an actual incident — automation matters most here.
9. Grievance officer designation and process. A named, reachable contact for grievances, with a documented resolution process. The designation itself is a decision a business makes; a platform's job is making sure grievances are actually tracked, escalated, and resolved within whatever timeline applies.
10. Continuously current audit documentation. A Record of Processing Activities that reflects reality, not a document rewritten twice a year from memory. This should be a byproduct of everything else running correctly — if a platform's consent, rights, and vendor tracking are genuinely connected, the ROPA updates itself.
11. Significant Data Fiduciary obligations, if applicable. DPIAs, annual audits, an Indian-resident DPO, algorithmic accountability — only relevant past certain volume and sensitivity thresholds, but worth checking against even if you don't think you've crossed them yet, because the threshold arrives faster than most businesses expect.
What this checklist actually reveals about automation's real role
Look back across those eleven items and a pattern shows up: automation handles the parts that are structurally about consistency and memory — tracking, scanning, escalating, documenting — extremely well. It doesn't replace the parts that are genuinely about judgment: whether specific notice language is adequate, whether a vendor's contract terms are legally sound, whether a grievance officer's decision on a disputed case was correct.
That split matters because a lot of vendor pitches blur it, implying a privacy management platform makes a business "compliant" the way flipping a switch would. It doesn't, quite. What it does is make the mechanical half of DPDP Compliance reliable enough that the judgment half — the part that actually needs a person — gets a team's full attention instead of being squeezed out by manual busywork.
DPDP compliance checklist: automatable vs. judgment-required
| Checklist Item | Platform Handles | Still Needs Human Judgment |
|---|---|---|
| Notice & purpose specification | Templating, versioning | Actual language and legal adequacy |
| Consent capture & withdrawal | Fully automatable | — |
| Immutable consent record | Fully automatable | — |
| Rights request tracking | Intake, SLA, escalation | Edge cases, identity verification |
| 48-hour pre-erasure notice | Fully automatable | — |
| Data discovery | Fully automatable (scanning) | Deciding retention/deletion policy |
| Vendor & DPA tracking | Expiry alerts, access flags | Contract terms adequacy |
| Dual-clock breach reporting | Fully automatable | Root cause and remediation decisions |
| Grievance process | Tracking and escalation | The actual grievance decision |
| Audit documentation (ROPA) | Fully automatable, if connected | — |
| SDF obligations | Workflow and deadline tracking | DPIA content, audit judgment |
Illustrative mapping of typical platform capability, not a specific vendor's feature audit.
How to actually use this checklist against a vendor
Don't just ask whether a privacy management platform "covers DPDP Compliance." Ask it against each item specifically. Does it template and version notices, or just host a static policy page? Does the 48-hour pre-erasure notice fire automatically, or is that a manual step someone has to remember to trigger? Does data discovery actually scan named databases, or is that a feature description without an underlying capability?
The gap between a platform that's genuinely built for this checklist and one that approximates it usually shows up in exactly this kind of specific question — not in the general marketing claim, which almost always sounds identical across vendors.
It's also worth revisiting this checklist periodically rather than treating it as a one-time audit. A new product feature adds a new data collection point. A new vendor gets onboarded. A business crosses into Significant Data Fiduciary territory without necessarily noticing the exact day it happened. DPDP Compliance isn't a status you achieve once — it's an operational state a business either maintains or quietly drifts away from.
Run this checklist against Consiva directly
Purpose-linked consent, immutable records, dual-clock breach tracking, self-updating ROPA — see exactly what's automated, free to start.
Start Free on Consiva.ai — No Credit Card →If you're working through this list against your own operations, Consiva's DPDP Act 2023 breakdown covers the statutory basis for each of these obligations directly, and the penalties and enforcement page is worth reading alongside it — not to create urgency for its own sake, but because knowing exactly what Schedule 1 attaches to each failure point makes it a lot easier to prioritise which checklist item to fix first. And if you're trying to work out where your own privacy management platform evaluation should start, the pricing page breaks down which of these checklist items sit in a free tier versus which require the fuller automated workflows.
A checklist is only as useful as what happens after you've read it. The honest next step isn't checking every box today — it's knowing exactly which ones are currently unchecked, and which of those a platform can close automatically versus which still need someone to actually decide something.
Frequently Asked Questions
Not a single official checklist document, but the Act, its Rules, and the Board's guidance together define specific, checkable obligations — consent, rights fulfilment, breach reporting, and documentation among them — which is what a thorough checklist should be built from directly.
No. It automates the mechanical, evidence-heavy parts reliably — consent records, rights tracking, breach clocks, documentation — but judgment calls on notice language, contract adequacy, and specific grievance decisions still require qualified legal or DPO involvement.
The 48-hour notice before erasure under Rule 8 is commonly missed. So is the dual-timeline breach reporting rule. They get overlooked because reminders do not happen on their own — nothing forces the step until a request is made or an incident shows up.
Continuously is ideal, but at minimum whenever a new data collection point, vendor, or product feature is introduced, and immediately upon any indication the business may be approaching Significant Data Fiduciary thresholds.
Start Free — No Credit Card
One domain, 1,000 cookie consents a month, unmetered rights requests, no expiry.