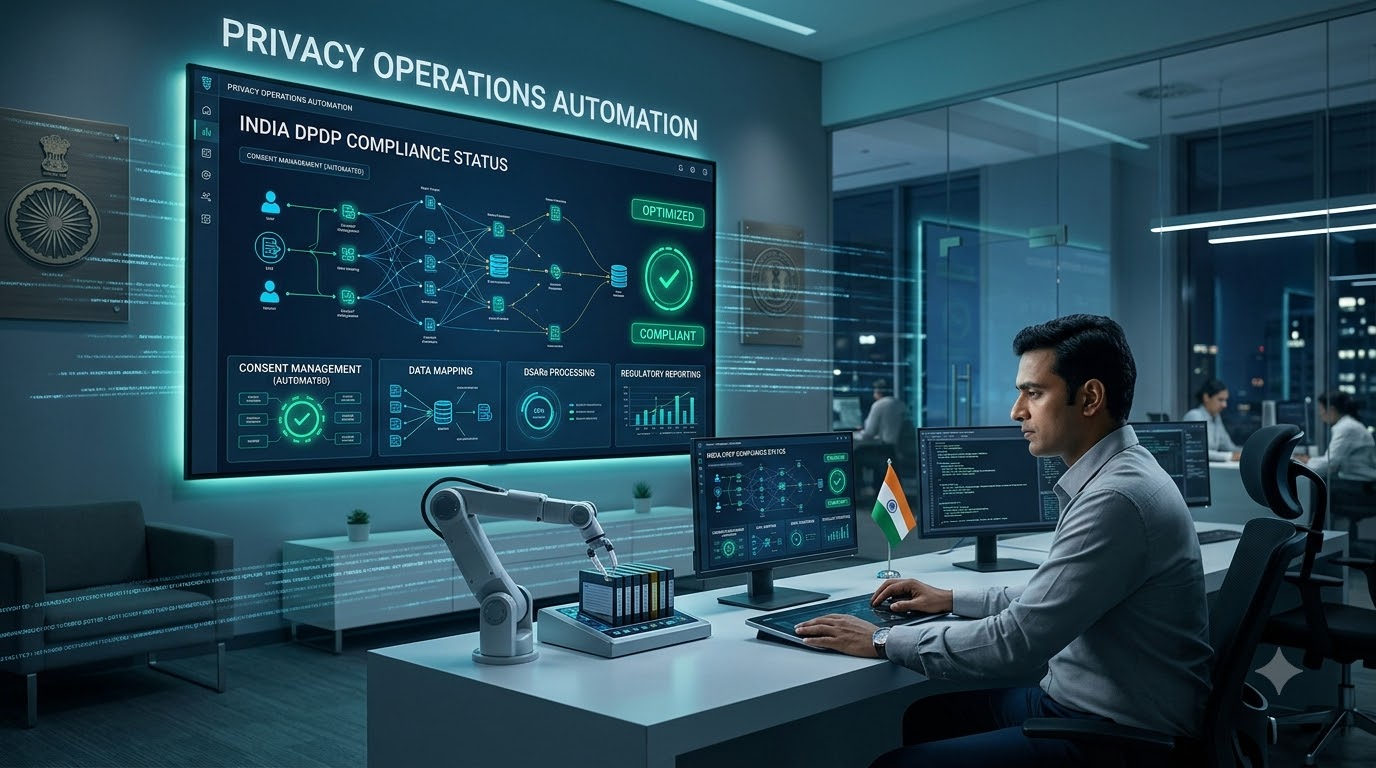
This is what privacy operations actually looks like at most companies — not a policy function sitting quietly in legal, but a genuine day-to-day operations job, closer to a support queue than a compliance checklist. And like any operations job running entirely on manual triage, it doesn't scale. It just gets slower and more error-prone as volume grows, until something slips through at exactly the wrong moment.
Privacy operations is an ops job, not a policy job
It helps to be clear about the difference. Legal writes the notice language and decides what's lawful. Privacy operations is the team that actually runs the machinery day to day — triaging incoming requests, tracking deadlines, coordinating with IT on data discovery, keeping the vendor register current, and making sure DPDP Compliance isn't just a stated intention but an observable, ongoing practice.
That distinction matters because operations problems need operations solutions. A policy gap gets fixed by rewriting a document. An operations gap — a request sitting untouched for six days because nobody was assigned to it — gets fixed by better workflow, not better wording. Automation belongs squarely in the second category, and treating privacy operations as a workflow problem rather than a policy problem is usually the first mental shift that makes automation actually useful instead of cosmetic.
Where automation actually changes a privacy operations team's day
The generic pitch for automation is "it saves time." True, but vague enough to be useless. Here's what it concretely changes for a team actually running privacy operations day to day.
Case triage stops being manual. Instead of someone reading every incoming request and deciding by hand who handles it, requests get automatically categorised — access, correction, erasure, grievance — and routed to whoever's queue has capacity, with priority weighting for anything close to its deadline.
SLA tracking becomes visible instead of remembered. Nobody has to hold "day nine of ten" in their head across forty concurrent requests. The system holds it, and it escalates before the deadline breaches rather than after someone happens to notice it already has.
Cross-team handoffs get a paper trail. When privacy operations needs IT to check whether a specific vendor still has database access, or needs legal to weigh in on a genuinely ambiguous erasure request, that handoff happens inside the same system, with a timestamp and an owner — not a Slack message that scrolls out of view by lunchtime.
Recurring compliance tasks stop depending on someone's memory. A quarterly vendor review, an annual policy refresh, a scheduled consent re-prompt cycle — these get triggered automatically instead of relying on someone's calendar reminder surviving a busy quarter.
Breach response gets a pre-built starting point. The moment an incident is logged, the relevant DPDP Compliance clocks start automatically, and a draft notification begins assembling itself from known facts, instead of someone opening a blank document while the clock is already running.
None of this replaces judgment. It replaces the specific failure mode where privacy operations depends entirely on someone's attention span holding up across dozens of simultaneous, deadline-bound tasks.
The maturity ladder: where most teams actually sit
Privacy operations automation isn't binary — either manual or fully automated. Most teams sit somewhere on a ladder, and it's worth being honest about which rung you're actually on before assuming the next step is out of reach.
Level 1 — Manual. Spreadsheets, shared inboxes, Slack threads. Every request tracked by memory and goodwill. This is where most teams start, and where a lot of teams stay far longer than they should, mostly because moving off it feels like a bigger project than it usually is.
Level 2 — Tracked. Requests land in one system with visible status, even if a human still does every step manually. This is a real improvement — visibility alone catches a surprising number of near-misses — but it's not automation yet.
Level 3 — Automated workflows. Routing, SLA escalation, and recurring tasks run without manual triggering. This is where privacy operations stops depending on any one person's bandwidth on any given day.
Level 4 — Predictive and proactive. The system flags risk before it becomes a deadline problem — an unusual spike in a specific request type, a vendor whose risk profile just changed, a consent cohort approaching its expiry window — surfaced ahead of time rather than discovered after.
What DPDP Compliance specifically demands from operations, not just policy
DPDP Compliance isn't satisfied by a well-written notice. It requires an operations team that can actually demonstrate specific things happening, on schedule, with evidence.
Sections 6 and 11 through 14 give data principals rights — withdrawal, access, correction, erasure, grievance, nomination — that a privacy operations team has to fulfil within a tracked window, not just acknowledge in principle. Rule 8's 48-hour pre-erasure notice requirement is a genuinely operational obligation — a scheduled job with a clock and an audit record, not a policy line. And the dual-clock breach structure, CERT-In's 6-hour window running alongside DPDP's own Board notification timeline, is precisely the kind of requirement that manual tracking handles badly under pressure and automated tracking handles as a matter of course.
None of this is optional documentation. It's operational proof, and privacy operations is the function that has to actually produce it.
Metrics worth tracking once automation is in place
| Metric | What It Reveals |
|---|---|
| Average time to first response | Whether triage is actually instant or still manually bottlenecked |
| Percentage of requests resolved within SLA | The real-world reliability of DPDP Compliance fulfilment, not just intent |
| Escalation rate before vs. after deadline | Whether automation is catching risk early or just logging misses after the fact |
| Cross-team handoff turnaround | Whether IT and legal responses are a bottleneck automation hasn't reached yet |
| Recurring task completion rate | Whether scheduled compliance tasks are actually happening or quietly slipping |
Illustrative metrics worth tracking, not a specific client's reported figures.
What to check before automating your privacy operations workflow
A few grounded questions worth asking before choosing a platform to build this around.
Does it handle DPDP Compliance's specific requirements — the dual breach clocks, the 48-hour pre-erasure notice, the Section 6/11–14 rights — as built-in workflows, or would your team need to configure these manually from a generic ticketing template?
Can it show a genuine escalation trail — who was assigned, when, and what happened if a deadline got close — rather than just a status field that says "pending"?
If you automate triage, does it really take work off your team's mind, or does it just shift the same calls into a prettier screen? The real question is what happens to a privacy ops analyst on a normal day. It is not about whether the tool seems more advanced.
SLA tracking that escalates itself
Consiva routes and escalates rights requests automatically, starts breach clocks the moment an incident's logged, and keeps a full handoff trail — free to start.
Start Free on Consiva.ai — No Credit Card →If your team is somewhere around Level 1 or 2 on that ladder, it's worth reading through Consiva's breakdown of Data Principal rights and duties to see exactly which obligations a privacy operations workflow needs to cover, and the 48-hour pre-erasure notice piece is a good concrete example of how a single DPDP Compliance requirement translates into an actual operational workflow rather than a policy sentence.
Privacy operations doesn't get easier by hiring more people to manually track more spreadsheets. It gets easier when the operational scaffolding — triage, SLA tracking, escalation, documentation — stops depending on any one person's memory holding up on a busy Tuesday.
Frequently Asked Questions
Policy work decides what’s lawful and writes the notice language. Privacy operations is the day-to-day function that actually runs the machinery — triaging requests, tracking deadlines, coordinating across teams — and is where automation has the most direct impact.
No. Automation handles routing, tracking, and escalation reliably; genuinely ambiguous cases — a disputed erasure request, an unclear processing basis — still need a person with legal or DPO judgment to decide.
If some requests get missed from time to time, and the team cannot see what is coming up, then manual methods are no longer doing the job. If key compliance steps rely on one person remembering to check a reminder, that is another sign to change the process.
Usually SLA tracking and escalation for rights requests — it's the highest-volume, highest-deadline-risk workflow for most teams, and the one where a missed deadline has the most direct DPDP Compliance consequence.
Start Free — No Credit Card
One domain, 1,000 cookie consents a month, unmetered rights requests, no expiry.