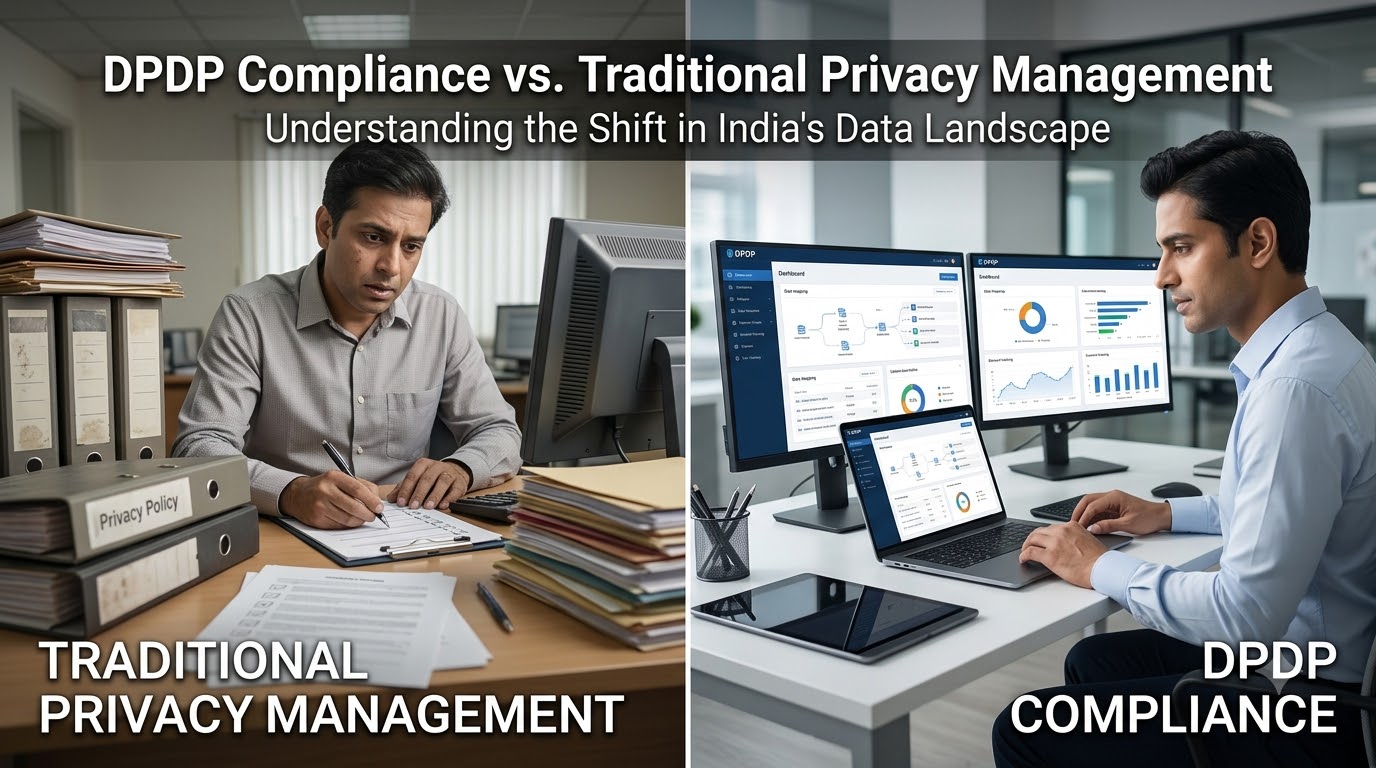
That's not a story about a careless company. It's the honest starting point for most Indian businesses right now, because "privacy management" in India, until very recently, meant something narrower and softer than what DPDP Compliance now actually requires. The gap between the two isn't cosmetic. It's structural, and a lot of businesses haven't fully registered how wide it's become.
What "privacy management" actually meant before DPDP
Before DPDP, Indian data protection law lived almost entirely inside Section 43A of the IT Act 2000 and the Sensitive Personal Data or Information Rules of 2011 — rules written for a much smaller, much less data-intensive internet. They covered "sensitive personal data" narrowly defined: passwords, financial information, health records, biometric data, sexual orientation. Everything outside that narrow list sat largely unregulated.
Consent, under the old regime, meant something close to a checkbox and a privacy policy link. There was no requirement for purpose-specific consent, no mandate for an immutable consent record, no statutory right to demand erasure. A company could collect broadly, retain indefinitely, and share fairly liberally, as long as its privacy policy technically disclosed the practice somewhere.
Enforcement was thin, too. Section 43A capped civil liability around unauthorised disclosure, but there was no dedicated regulator, no dedicated grievance mechanism a citizen could actually invoke, and no breach notification requirement at all. A data breach could happen, and unless it became a media story, there was no legal obligation forcing a company to tell anyone.
DPDP Compliance replaces all of this with something categorically different — not an update to the old framework, but a genuinely new one.
What actually changed, point by point
A dedicated regulator now exists. The Data Protection Board of India didn't exist under the old regime. It now investigates complaints, issues penalties, and gives individuals somewhere concrete to escalate a grievance, instead of a theoretical civil remedy nobody realistically pursued.
Consent became purpose-specific and provable. DPDP Compliance requires consent tied to a specific stated purpose, in clear language, with a genuine ability to withdraw it — and a company needs to be able to prove what was actually consented to, not just point to a policy page that existed at signup.
Individuals now have enforceable rights. Access, correction, erasure, grievance redressal, and nomination — DPDP gives Indian data principals rights that simply didn't exist in enforceable form before. Under the old regime, asking a company to delete your data was a request with no statutory teeth behind it.
Breach notification is now mandatory, not optional. This is one of the sharpest changes. Previously, a breach might never require disclosure at all. Under DPDP, notification obligations exist, and — for businesses also covered by CERT-In's Directions — a second, faster 6-hour reporting clock runs independently alongside DPDP's own window.
Penalties moved from theoretical to genuinely severe. The old regime's liability ceiling was modest enough that many companies treated it as a cost of doing business. DPDP's penalty structure reaches up to ₹250 crore per violation category — a number designed to actually change board-level risk calculus, not sit quietly in a footnote.
The law now follows the data, not the company's address. DPDP applies to any entity processing personal data of individuals in India, regardless of where that company is headquartered. A US or European SaaS company with Indian users is now squarely in scope in a way the old regime never quite reached.
A "Significant Data Fiduciary" category exists for the first time. Companies crossing certain thresholds of volume, sensitivity, or risk now face materially heavier obligations — a mandatory Indian-resident DPO, DPIAs, annual audits — categories the old regime had no equivalent for at all.
Traditional privacy management vs. DPDP Compliance
| Dimension | Traditional (IT Act / SPDI Rules) | DPDP Compliance |
|---|---|---|
| Dedicated regulator | None | Data Protection Board of India |
| Consent standard | Broad, policy-disclosure based | Purpose-specific, provable, withdrawable |
| Individual rights | Largely theoretical | Access, correction, erasure, grievance, nomination |
| Breach notification | Not mandated | Mandatory, dual-clock with CERT-In |
| Penalty ceiling | Modest civil liability | Up to ₹250 crore per violation category |
| Extraterritorial reach | Limited in practice | Applies regardless of company's location |
| Large-scale processors | No special category | Significant Data Fiduciary — added obligations |
Illustrative comparison based on the regulatory frameworks as publicly notified, not a specific client's compliance assessment.
What actually still carries over, and what has to be rebuilt
It's not that everything from before is worthless. A well-drafted vendor contract with genuine data processing clauses is still useful scaffolding — it just needs updating to reflect DPDP-specific obligations rather than replacing entirely. Existing security practices, encryption standards, and access controls remain relevant; DPDP builds obligations on top of reasonable security practices, it doesn't invent the concept.
What genuinely needs rebuilding, though, is the operational layer underneath the policy documents. A privacy policy that technically discloses broad data use doesn't satisfy DPDP Compliance's purpose-specific consent requirement. A vendor spreadsheet nobody's updated in a year doesn't meet the bar a Data Protection Board investigation would actually apply. And "we've never had a formal breach reporting process" stops being a quietly acceptable gap the moment mandatory notification becomes law.
The businesses struggling most right now are the ones assuming DPDP Compliance is a documentation update — swap the privacy policy language, done. It isn't. It's an operational rebuild of consent capture, rights fulfilment, and breach response, dressed in the same-looking website footer link that was already there.
What this actually means for a business right now
The practical question isn't whether your old privacy policy was fine under the old regime — it probably was, by that regime's fairly low bar. The question is whether your current operations can withstand a Data Protection Board inquiry, a genuine rights request at volume, or a breach that now legally has to be reported within hours, not quietly absorbed.
Prove it, not just disclose it
Consiva captures provable, purpose-specific consent, automates rights fulfilment, and runs both DPDP and CERT-In breach clocks — free to start.
Start Free on Consiva.ai — No Credit Card →If you're still relying on a privacy policy written for the SPDI Rules era, or if "compliance" internally still means "we have a document," it's worth reading Consiva's breakdown of the DPDP Act 2023's actual scope and provisions directly, alongside the specific data fiduciary obligations under Sections 4 through 10 that replace the old, much thinner disclosure standard. And if there's any lingering assumption that enforcement is still theoretical the way it was under the old regime, Is DPDP Enforceable Yet? What the Gazette Actually Says is worth reading before assuming there's more runway than there actually is.
The old regime asked companies to disclose what they did with data. DPDP Compliance asks them to prove it, on demand, with consequences attached that actually bite. That's the real shift — not a new document, a new operating standard.
Frequently Asked Questions
Not really. It replaces the old Section 43A / SPDI Rules framework with a dedicated regulator, enforceable individual rights, mandatory breach notification, and penalties severe enough to change board-level risk decisions — a structurally different regime, not an amendment.
No. Purpose-specific consent, provable consent records, rights fulfilment workflows, and mandatory breach notification are new obligations the old framework never required, regardless of how thorough a company's previous privacy policy was.
Yes. DPDP applies based on whether a company processes personal data of individuals in India, not where the company is headquartered or incorporated — a meaningfully broader reach than the old regime typically enforced in practice.
Usually the operational shift from policy documentation to provable process — being able to show a specific consent record, respond to a rights request within a tracked deadline, and report a breach within hours rather than treating disclosure as optional.
Start Free — No Credit Card
One domain, 1,000 cookie consents a month, unmetered rights requests, no expiry.